Apple Adds My SMB Vulnerability Credit After Release - CVE-2026-86871
Apple fixed an SMB vulnerability I reported in macOS Golden Gate 27. Apple later acknowledged the report when it added CVE-2026-86871 to its security advisories on October 19, 2026. The fix was also included in macOS Tahoe 26.7 and macOS Sequoia 15.8.
CVE-2026-86871 - SMB
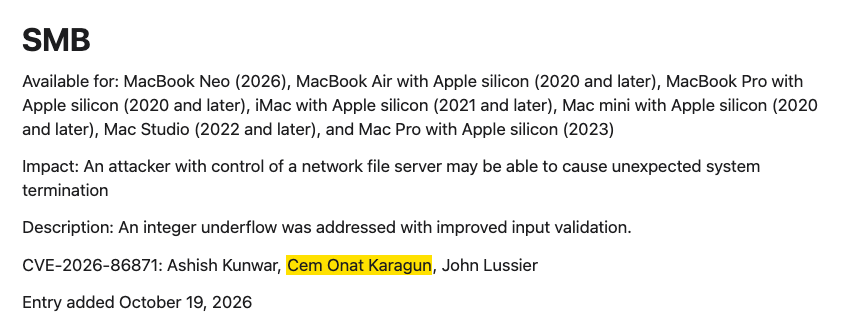
The attack vector was network-based.
Apple awarded my report a bounty. Based on that award, I believe I was the first eligible reporter, although the advisory does not publish the reporting order.