tsMuxer Vulnerability Disclosure: 7 Memory Safety CVEs I Reported
In May 2021, I reported 7 vulnerabilities in tsMuxer. 5 were heap-based buffer overflows, 1 was an out-of-bounds read, and 1 was a divide-by-zero issue. Each report included a proof-of-concept file and sanitizer output. Some also included root-cause analysis, including my analysis and fix for CVE-2021-34070.
tsMuxer is a C++ transport-stream muxer. It was also used by Universal Media Server (archived page).
The project merged fixes for all seven reports on June 9, 2021. The first five CVEs were published on June 23. CVE-2021-35344 and CVE-2021-35346, the final two records, were published on December 3, 2021.
Vulnerabilities
The issues are listed in the order I reported them.
- CVE-2021-34071 - Heap-based buffer overflow. Reported in issue #423 on May 22 and fixed by commit
ea879f3b. - CVE-2021-34067 - Heap-based buffer overflow. Reported in issue #424 on May 22 and fixed by commit
d77ed5e8. - CVE-2021-34070 - Out-of-bounds read. Reported in issue #426 on May 24 and fixed by commit
378377e9. - CVE-2021-34068 - Heap-based buffer overflow. Reported in issue #427 on May 24 and fixed by commit
ea879f3b. - CVE-2021-34069 - Divide-by-zero. Reported in issue #428 on May 24 and fixed by commit
9070a991. - CVE-2021-35344 - Heap-based buffer overflow. Reported in issue #432 on May 27 and fixed by commit
8028fb84. - CVE-2021-35346 - Heap-based buffer overflow. Reported in issue #436 on May 27 and fixed by commit
d77ed5e8.
Root Cause and Fix for CVE-2021-34070
For CVE-2021-34070, I went beyond the sanitizer crash and traced the root cause in the VC-1 parser. An attacker-controlled value could select index 7 from a table that contained only five entries. I provided a proof-of-concept fix that added the missing bounds checks.
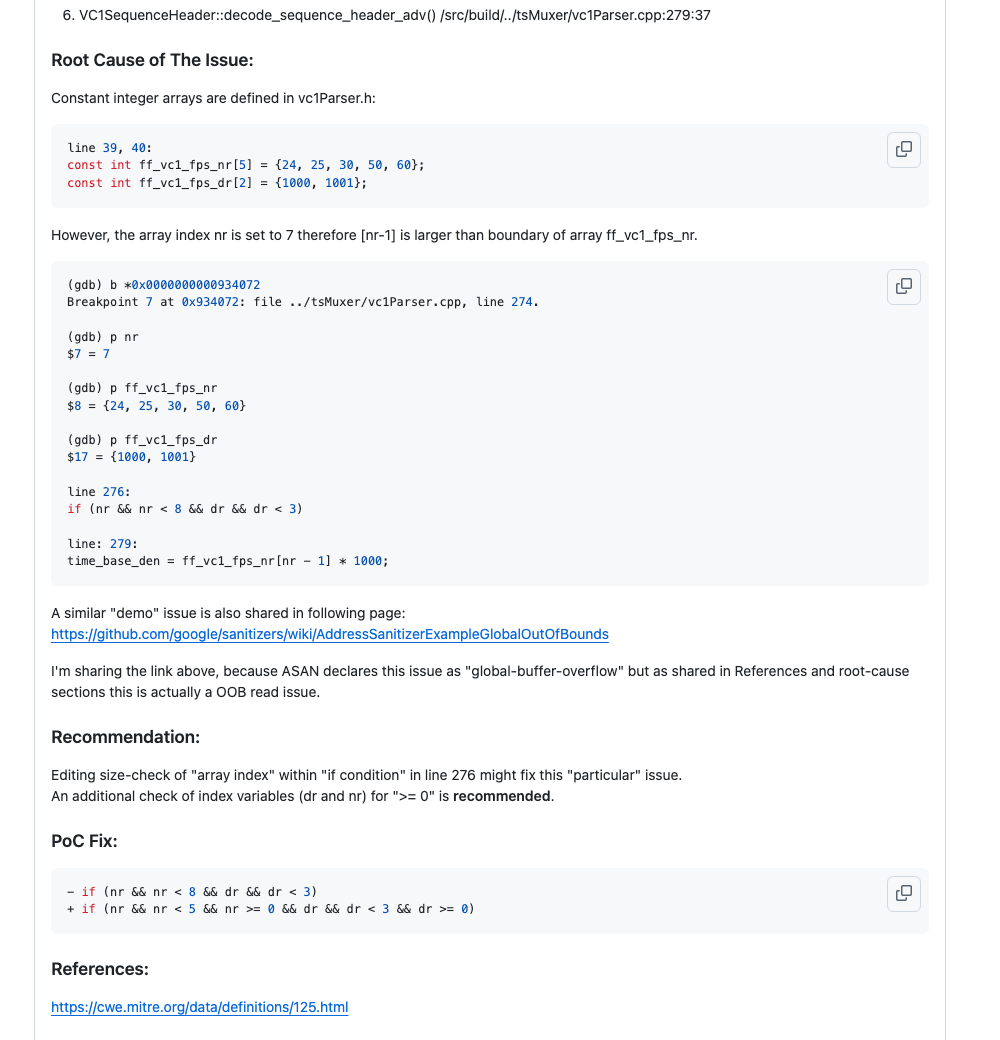
The maintainer noted that this code originated in FFmpeg and said he would push the fix. The merged patch used the bounds-checking direction from my report while also restoring the two missing frame-rate values from the FFmpeg table.